Nops reads SOPS-encrypted files straight into .NET configuration. No sops binary, no subprocess, no plaintext on disk.
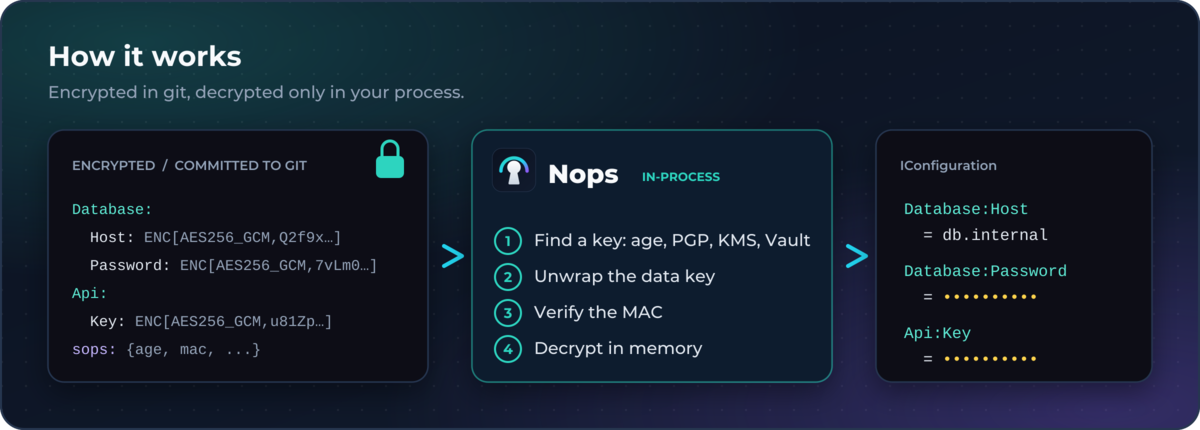
You keep encrypting and editing secrets with the sops CLI and commit the encrypted files. Your app decrypts them in-process at startup:
builder.Configuration.AddSops("secrets.sops.yaml");
Install
dotnet add package Nops.Configuration   # IConfiguration provider (includes Nops.Core)
dotnet add package Nops.Core            # Decryption API only
Why Nops
Formats and keys
Where next
- Quickstart: first decrypt, typed binding, samples
- Configuration reference: every option, key flattening, reload, errors
- Deploying with Nops: config layout, Kubernetes and Docker, key rotation, troubleshooting
- Hosting guide: console, worker service, ASP.NET Core and Azure Functions
- Docker and distroless images: run without a shell or the sops binary
- Kubernetes and GitOps: how Nops fits with Flux and Argo CD
- Migrating to Nops: from
sops -d, user-secrets and environment variables - Comparison: the other ways to use SOPS from .NET
- Security model: guarantees, verification and limits
- Cloud KMS setup: AWS, GCP, Azure Key Vault, HashiCorp Vault
- API reference: every public type